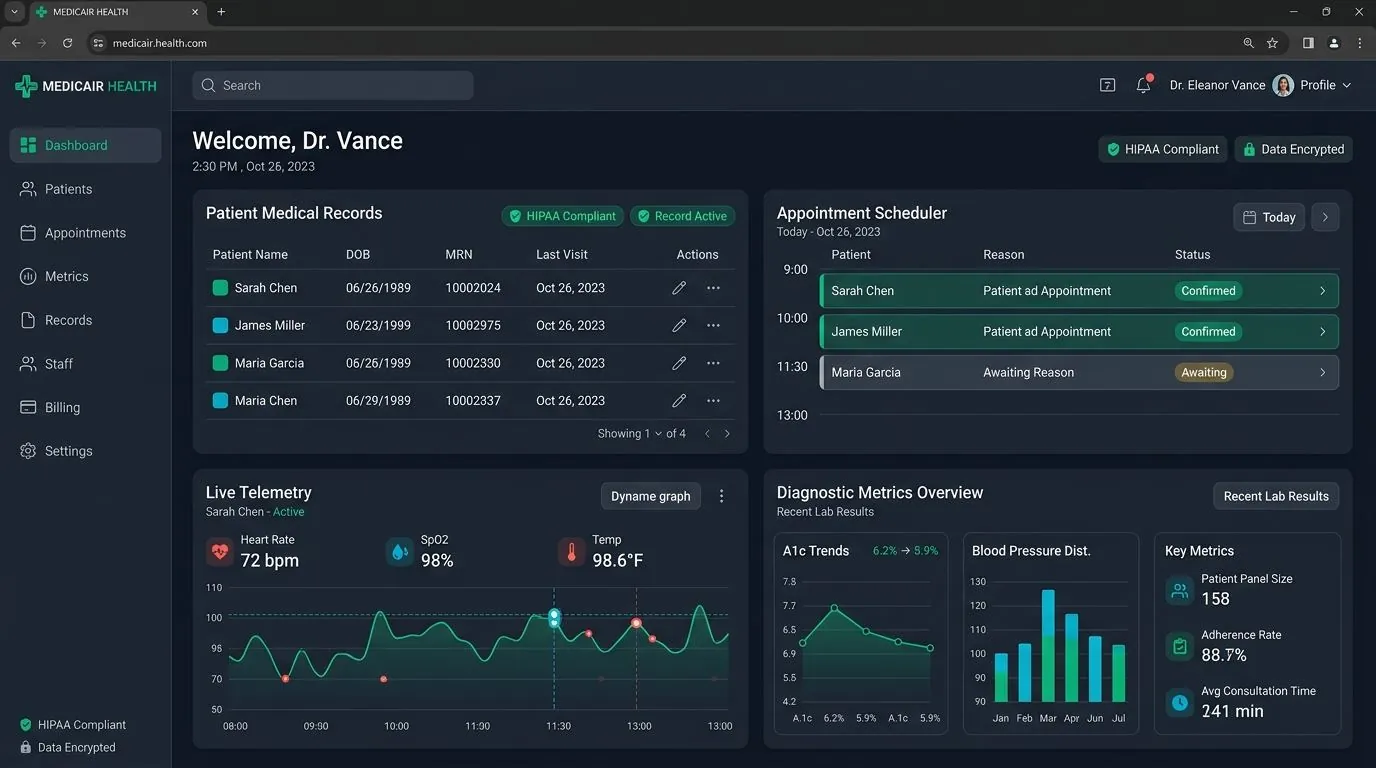
One secure system for patient records, staff workflows and appointment booking, with HIPAA-compliant protection (the US standard for health data) and 99.95% uptime.
Overview
What this is and why it matters, in plain English.
One secure system for patient records, staff workflows and appointment booking, with HIPAA-compliant protection (the US standard for health data) and 99.95% uptime.
Healthcare admin platform where each role sees only what it should, and records open in under 85ms.
The situation
What was going on before, and why it needed fixing.
Patient appointments, medical records and billing lived in separate databases. Every screen that needed all three stitched them together at request time, and queries regularly ran past 900ms.
The platform also carried protected health information, so any redesign had to tighten access and encryption at the same time it made things faster.
Healthcare organizations handled patient appointments, medical records, and billing with fragmented databases, leading to query lag over 900ms and compliance risks.
What it needed to do
The outcomes the project had to deliver.
- Bring records, scheduling and billing onto one encrypted data layer.
- Give doctors, nurses, administrators and patients exactly the access their role needs, and log everything else.
- Keep record and schedule queries under 100ms on a multi-tenant workload.
What I did
My part of the work and who I worked with.
I led the backend: the Laravel API, the RBAC and audit model, the AWS RDS schema and indexing, and the Redis caching layer. I worked with the Angular team on the role-aware screens and with operations on backups and failover.
How it works
The main building blocks, from the screen people use to the data underneath.
Engineered an end-to-end encrypted architecture on AWS RDS (PostgreSQL/MySQL) with Redis caching layers, granular Role-Based Access Control (RBAC), and automated backup strategies.
- 01
Angular client
Role-aware screens for practitioners, front desk and patients. The UI only renders actions the API will allow, but it never relies on that for security.
- 02
Laravel API and middleware
Every patient route passes through an authorization middleware that checks the permission for the healthcare guard, writes unauthorized attempts to the audit log, and derives a short-lived decryption key for the request.
- 03
AWS RDS (MySQL/PostgreSQL)
Patient, appointment and billing tables consolidated with encryption at rest and composite indexes shaped around the real query patterns: by practitioner and day, by patient and date range.
- 04
Redis and Node.js workers
Hot reads such as today’s schedule are cached in Redis with tenant-scoped keys. Node.js workers handle notifications and background jobs off the request path.
Key choices and trade-offs
Every build involves trade-offs. These are the important ones and what each one cost.
| Decision | Trade-off |
|---|---|
| Permission checks in middleware, not in controllers. | Every route pays a small authorization cost, but no endpoint can forget to check, and the audit trail is uniform. |
| Tenant-scoped cache keys in Redis. | More keys and slightly lower hit ratio across tenants, in exchange for zero chance of one clinic reading another’s cached data. |
| Ephemeral per-request decryption keys. | Extra key-derivation work per request, but long-lived keys never sit in application memory. |
Under the hood
Implementation details for technical readers, with a code sample.
- A single authorization middleware covering every patient route, with audit logging of denied access.
- Consolidated encrypted schema on AWS RDS with automated backups.
- Indexes designed from query plans rather than guesses, keeping reads under the 85ms target.
// HIPAA Authorization & Encrypted Patient Access Middleware
class EnsureAuthorizedPractitionerAccess {
    public function handle(Request $request, Closure $next, string $requiredPermission) {
        $user = $request->user();
        if (!$user || !$user->hasPermissionTo($requiredPermission, 'healthcare')) {
            AuditLogger::logUnauthorizedAccessAttempt($user, $request->route('patient_id'));
            return response()->json(['error' => 'Forbidden Access to Medical Record'], 403);
        }
        $request->attributes->set('decrypted_vault_key', KMSVault::deriveEphemeralKey($user->id));
        return $next($request);
    }
}
Problems solved
What got in the way, and how each problem was fixed.
- 01
Ensuring strict HIPAA data governance and end-to-end encryption for at-rest and in-transit patient telemetry.
Encryption at rest on RDS, TLS everywhere in transit, and per-request key derivation so decrypted data only exists for the life of the request.
- 02
Fine-grained role authorization policies differentiating medical doctors, nurses, administrators, and patients.
A permission model keyed by role and resource, enforced in middleware and mirrored in the UI, with denied attempts written to the audit log.
- 03
Database indexing optimization maintaining sub-100ms queries under heavy multi-tenant loads.
Composite indexes per access pattern plus Redis for the hottest reads, verified with query plans under multi-tenant load.
Security, speed and growth
How data is protected, and how the system stays fast as usage grows.
Security
HIPAA-aligned data governance: encryption at rest and in transit, least-privilege roles, audit logging of access attempts, and automated backups. Patient data is never cached under a key that is not tenant-scoped.
Speed & growth
Query latency stays under 85ms through indexing and Redis caching, and the platform runs at 99.95% uptime. Background work moves to Node.js workers so request latency stays flat during heavy periods.
Quality and releases
How changes were tested and shipped safely.
Feature tests cover every role against every protected route, including the denied cases. Query plans for the main screens are checked as part of review, and backup restores are rehearsed rather than assumed.
Tech stack
The tools and technologies used, for recruiters and technical reviewers.
Results
Measured outcomes recorded for this project.
| Metric | Result |
|---|---|
| Query Latency | <85 ms |
| Uptime Reliability | 99.95 % |
| Compliance Grade | HIPAA verified |
Questions
Plain answers first, then the detail a technical reviewer would ask about.
Common questions
- What problem did this solve for the clinic?
- Records, appointments and billing were in separate systems, so screens were slow and access was hard to control. Now staff work in one secure system where each role sees only what it should, and records open in under 85ms.
- Could you build something similar for my practice or health startup?
- Yes. Healthcare platforms with patient records, scheduling and strict access rules are a core part of my experience. Get in touch to discuss scope and pricing.
For your tech lead
- How is access separated between roles?
- Each role maps to a set of permissions on the healthcare guard. The middleware checks the required permission on every patient route and logs any denial.
- What keeps queries fast?
- Composite indexes built around the real access patterns, plus Redis caching for hot reads like the daily schedule.
- Is patient data cached?
- Only under tenant-scoped keys, so one clinic can never read another clinic’s cached data.
Key takeaways
- •Healthcare admin platform where each role sees only what it should, and records open in under 85ms.
- •Built with Laravel, Angular, AWS RDS, Node.js, Redis, MySQL, HIPAA.